WebParam perspective | October 2026
A voice note appears to come from a director. A supplier email says its bank details have changed. Both ask the finance team to act before the afternoon payment run.
The messages might be genuine. The risk is that a familiar voice, writing style or sender name is no longer enough to prove who made the request. The decision that matters is not whether a colleague can spot a convincing fake. It is whether the business has a dependable way to verify a consequential change before acting on it.
October is Cybersecurity Awareness Month in South Africa. The Cabinet's September 2026 statement names the observance as a prompt for digital safety and resilience. It does not claim that a particular kind of fraud is surging. The business question for this month is more specific: what happens when a request looks authentic but would move money, change access or release information? [1]
Why the old cues are weak
Fraudsters have long impersonated executives and suppliers. In its 2024 crime report, the South African Banking Risk Information Centre (SABRIC) described business email compromise cases involving urgent payment requests and altered bank details. Those cases do not all involve AI. [2]
Generative tools can add another layer of plausibility. The FBI has warned that criminals can use generated audio to impersonate a person and ask for payment. That is evidence of a possible technique, not a measure of how often it happens in South African businesses. [3]
An email can carry the right signature. A voice note can sound familiar. A caller may know the name of a real project or invoice. None of those details should be the final authorisation for a change to a bank account, payroll record, system permission or sensitive data transfer.
Make the trigger about the action, not the message
A useful verification rule names the actions that must pause. It should apply regardless of who seems to be asking or which channel they use.
Start with a short list:
- A new or changed supplier bank account.
- An unusual payment, refund or payroll instruction.
- A request to grant access, share credentials or disclose a sensitive document.
- A request to bypass an established approval or verification step because it is “urgent.”
The trigger is the requested change. Staff do not have to decide whether a voice was cloned or an email was forged before they use the rule. This avoids turning every payment clerk into a forensic analyst.
Verify through a route you already trust
When a trigger appears, pause the transaction and contact the person or supplier through a number or channel already held in a trusted record. Do not use the phone number, link or reply address supplied in the new request. Confirm both the identity and the exact change: the account details, amount, beneficiary or access being requested.
For a supplier bank-detail change, the business might call a contact listed in its existing supplier master record, then require a second authorised person to approve the change before the next payment. If the known contact is unavailable, the request waits. Urgency is a reason to escalate the verification, not skip it.
This approach matches public guidance to verify suspicious requests using a known contact method rather than replying through the original message. [4]
Keep a record of who verified the request, which trusted route they used, what details were confirmed and who approved the final action. The record should be short enough for staff to complete during normal work, but clear enough to reconstruct a decision later.
Design the workflow so the pause is real
A policy that says “be careful” can disappear under deadline pressure. The operational workflow should make the safer action easy.
For example, a bank-detail change can create a verification task, hold related payments and prevent the same person from both changing and approving the account. A high-risk access request can require an owner and expiry date. An exception path can identify who takes over when the usual approver is away, while still requiring an independent check.
Automation can help route and document these steps. An AI tool might classify incoming requests or highlight a change in account details. It should not be the sole authority deciding that a voice, sender or document is genuine. The final control is an independently verified instruction and an accountable approval.
The design has to fit the business. A two-person approval that exists only on paper will not help if both people rely on the same unverified email thread. Separate the evidence used to initiate a request from the evidence used to approve it.
Rehearse one ordinary case and one awkward case
Test the process with a routine supplier update. Can the team find the trusted contact quickly? Can it record the call and release the payment without unnecessary delay?
Then test the awkward version: a convincing voice note arrives just before cutoff, the usual approver is travelling, and the supplier says the old account has closed. The process should tell staff who can verify, who can approve and when to stop. If the answer depends on one person's memory, the workflow needs work.
If money has already moved or access has been granted on a suspicious instruction, stop further action, contact the bank or relevant service provider promptly, alert the internal security owner and preserve the original messages and approval record. Response steps should be set before an incident, while everyone can still think clearly.
Trust is a process
At WebParam, we would start by mapping the decision points in a real workflow: where a request arrives, what change it can cause, who verifies it and which system records approval. That work may point to a simpler process change, an integration or a carefully scoped automation. The outcome should be a process staff can follow under pressure.
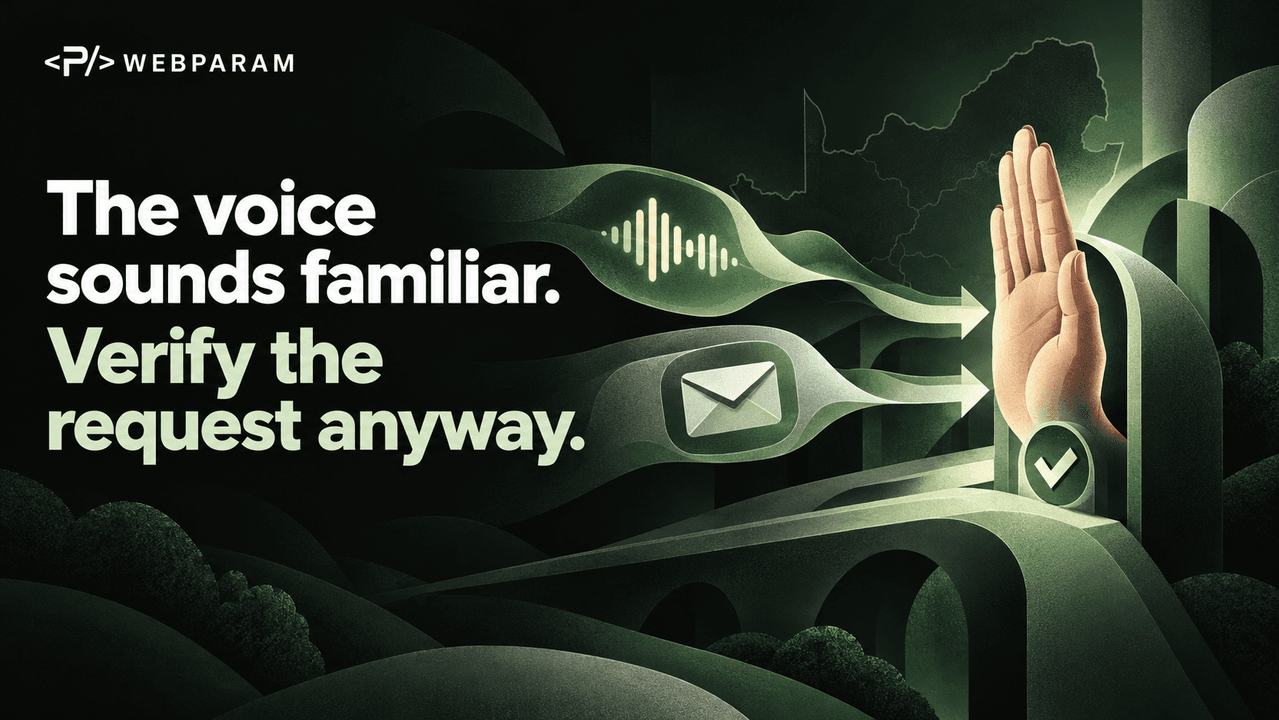
The lesson of the image is deliberately simple: the voice can sound familiar, and the request can still wait for verification. In October, that is one practical way to turn cybersecurity awareness into a stronger business habit.
Sources
- South African Government, Cabinet statement of 23 September 2026, published 29 September 2026, section on Cybersecurity Month.
- SABRIC, Annual Crime Statistics 2024, section on executive impersonation and payment fraud.
- FBI Internet Crime Complaint Center, Criminals Use Generative Artificial Intelligence to Facilitate Financial Fraud, 3 December 2024.
- CISA, Four Cybersecurity Essentials, guidance on verifying through a known contact method.